
 0
 0
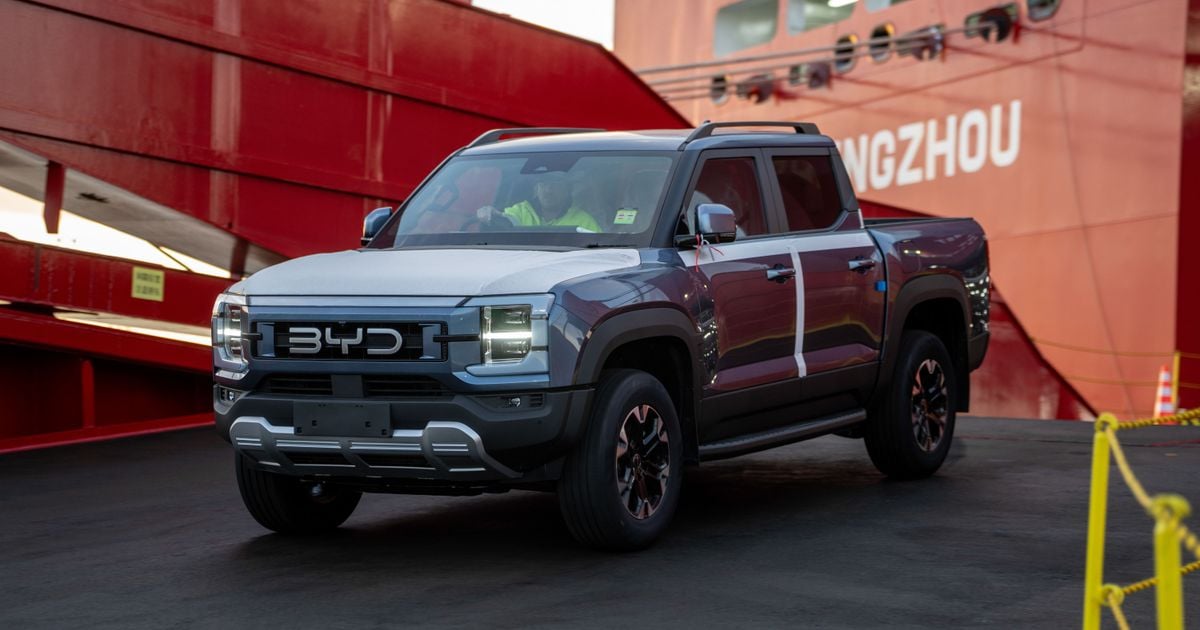
BYD Australia will make upgrades to the software program in its Shark 6 plug-in hybrid ute following its personal inside investigation into the hacking of one among its dual-cabs for ABC present affairs program Four Corners.
The report made headlines after a BYD Shark 6 ute was accessed by Canberra-based Fortify Labs, which accessed the automobile’s infotainment software program to observe its location and even tapped into cellphone calls made within the automobile.
Four Corners additionally confirmed the automobile’s headlights and windscreen wipers being accessed remotely by skilled hackers, demonstrating vulnerabilities within the automobile’s software program.
Following this system, which was broadcast on September 21, 2026, BYD Australia launched a proper inside investigation into the claims.
The Chinese automaker mentioned the investigation discovered the flexibility to entry the automobile was the results of a ‘software defect’ in its infotainment software program, exploited utilizing an ‘Android Debug Bridge’ (ADB), a device which permits entry to Android units.
The BYD Shark 6 makes use of a ‘DiLink’ infotainment system primarily based on Android software program, utilized in different BYD and Denza fashions offered in Australia, though it is closely customised and developed particularly by BYD.
“The researcher exploited a software defect to enable the ADB and subsequently install an untrusted third-party application,” mentioned BYD in an announcement.
It mentioned particular instruments had been required to entry the ADB, and the corporate’s engineers had been in a position to replicate the actions proven on Four Corners as a part of the investigation.

However, BYD mentioned the preliminary entry to the automobile required bodily entry and could not be carried out remotely.
“When the application requested access to certain information or functions, such as the vehicle’s location or microphone, the infotainment system displayed a permission prompt,” the BYD assertion mentioned.
“The requested permissions could only be granted after the user manually approved the request through the infotainment interface.
“The corrective action will address the identified ADB-related software issue and remove the unintended pathway that allows ADB to be enabled through the infotainment system user interface, thereby eliminating the access path identified during the investigation,” the assertion mentioned.
BYD will deploy an over-the-air software program replace for the Shark 6 “only once the updated software has undergone rigorous validation [testing]”. It says it is also investigating if this replace can be required for different fashions in its lineup.
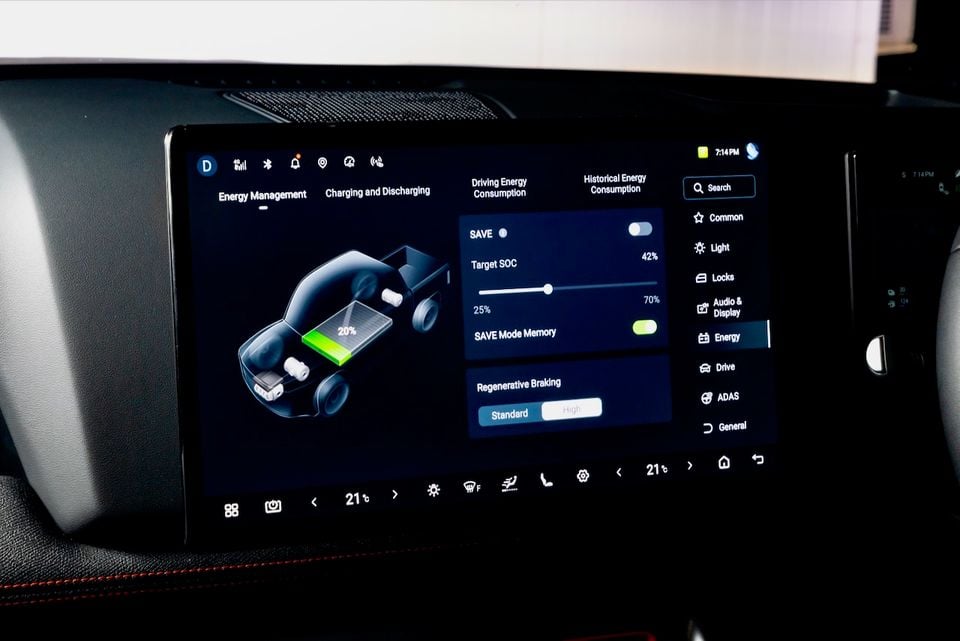
The different space BYD investigated was entry to the automobile’s controller space community (CAN), or ‘CAN bus’. A CAN bus is the inner communications community that permits the automobile’s digital management models and different methods to speak with one another, primarily appearing because the automobile’s nervous system.
This is how Fortify Labs remotely accessed the headlights and different features of the Shark 6 for Four Corners.
“BYD’s technical analysis has confirmed that the demonstrated control of the vehicle’s headlights and windscreen wipers required direct physical access to the vehicle’s internal CAN bus by tapping into the vehicle wiring,” the automaker mentioned.
“This method requires physical intervention on the target vehicle and is limited to the individual vehicle that has been physically accessed.”
The company says it has initiated a “dedicated risk assessment” to assess the “necessity and technical feasibility of additional measures relating to CAN message authenticity, integrity and freshness verification”. It says it’ll use findings to “further review and strengthen relevant cybersecurity controls and development processes”.
“BYD has implemented security measures for the OBD interface, including device authentication and physical isolation, and has established corresponding cybersecurity safeguards in accordance with the requirements of UN R155,” the company said.
UN R155 requires automakers to operate a Cyber Security Management System (CSMS), which identifies potential vehicle cybersecurity risks and requires appropriate measures to manage and mitigate those vulnerabilities.
Draft Australian Design Rules ADR 115 and ADR 116, designed to better regulate vehicle security, are based on UN R155 and UN R156, but timing for the introduction of the new ADRs has not yet been finalised.
Fortify Labs has issued a statement of its own, saying its objective for the Four Corners episode was to “Simulate the remote access a car manufacturer has to a connected vehicle and demonstrate how this access could be abused”.
“It is important to highlight that at no point was this investigation about gaining initial access to the vehicle,” the organisation said.
“The required access was already implied, given we were simulating a manufacturer’s access to a connected vehicle. Manufacturers have the ability to reach into their vehicles remotely, run individual commands and deliver over-the-air (OTA) updates.”
Fortify Labs did commend BYD for well-implemented security in parts of the vehicle, but said it hoped its demonstration of vulnerabilities would be a catalyst for change, and noted the draft ADRs are a step in the right direction.
It has called for a cybersecurity star rating for consumers to evaluate the security of connected cars, including data storage and collection.
“People shouldn’t just blindly trust that vehicle manufacturers are producing safe and secure cars, and this doesn’t only apply to Chinese manufacturers. The same goes for vehicles coming out of the United States, Europe and the rest of Asia. It applies to all vehicle manufacturers,” it said.
“It’s also worth highlighting that these risks are not faced by Australia alone. This is a global issue, and other countries should be concerned.”
MORE: ‘Urgent’ requires higher transparency on information assortment following report on Chinese automobile hacking
Source link
#BYD #Shark #hacking #investigation #reveals #software program #defect


