
 0
 0
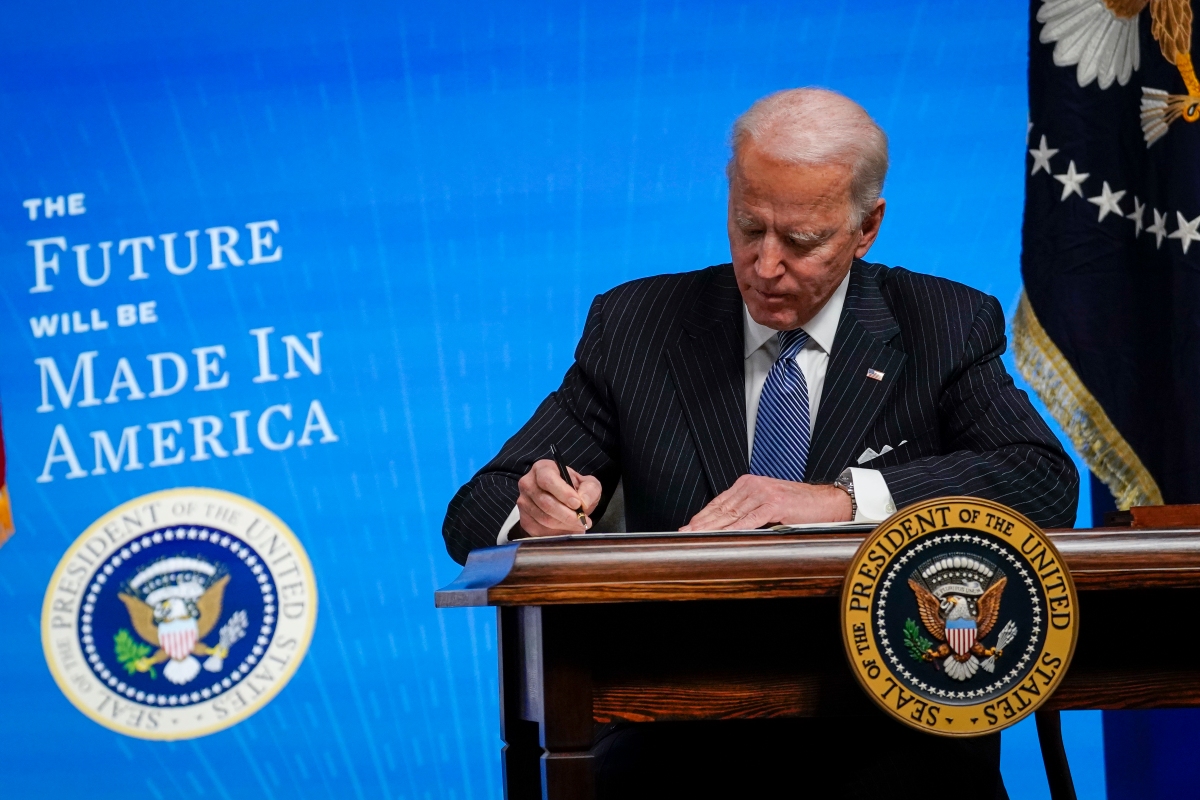
U.S. president Joe Biden has signed an govt order connected to reupping a flagship information switch settlement with the European Union — with the aim of creating life simpler for companies that have to export EU user-data to the U.S. for processing.
The White House introduced the event in an announcement at present — saying that the “Executive Order on Enhancing Safeguards for United States Signals Intelligence Activities” would “direct the steps” that the U.S. will take to implement its commitments beneath the EU-U.S. Data Privacy Framework (EU-U.S. DPF), as the brand new association is being referred to as.
The new framework is meant to interchange the defunct EU-U.S. Privacy Shield (which was invalidated by the bloc’s high court docket again in July 2020); and its a lot longer-lived predecessor, Safe Harbor (struck down by the CJEU in October 2015, following the 2013 disclosures of U.S. authorities surveillance applications by NSA whistleblower, Edward Snowden).
So that is yet one more (third time fortunate?) try and bridge the hole between two very totally different authorized frameworks with a view to be sure that EU customers’ private information can hold flowing over the pond.
Thousands of companies, giant and small, had relied upon earlier EU-U.S. information switch offers to authorize their information exports — greasing the pipes of what the White House refers to as a $7.1TR EU-U.S. “economic relationship”.
But for the final two years there’s primarily been no risk-free authorized route. And there nonetheless isn’t.
Although the EU responded to Biden signing the EO by saying it should now transfer to draft an adequacy choice and provoke the adoption course of.
‘Safeguards for signals intelligence’
The White House press launch stated president Biden’s govt order beefs up safeguards round U.S. “signals intelligence” (aka digital surveillance carried out by spy companies) by “requiring that such activities be conducted only in pursuit of defined national security objectives”; by “tak[ing] into consideration the privacy and civil liberties of all persons, regardless of nationality or country of residence; and by being “conducted only when necessary to advance a validated intelligence priority and only to the extent and in a manner proportionate to that priority”.
The EO additionally mandates “handling requirements” for private information picked up through indicators intelligence and beefs up enforcement round non-compliance. Elements of the US Intelligence Community can even be required to replace their insurance policies and procedures to replicate the “new privacy and civil liberties safeguards contained in the E.O.”, per the press launch.
Another change is the creation of “a multi-layer” redress mechanism for EU people within the EU to acquire “independent and binding review and redress” on claims that their private information was gathered in violation of relevant U.S. legislation.
This consists of — within the first layer — a Civil Liberties Protection Officer (CLPO) within the Office of the Director of National Intelligence who will conduct a preliminary investigation “of qualifying complaints received ” to determine whether or not there was a violation and, if that’s the case, decide acceptable subsequent steps.
“The E.O. builds up the existing statutory CLPO functions by establishing that the CLPO’s decision will be binding on the Intelligence Community, subject to the second layer of review, and provides protections to ensure the independence of the CLPO’s investigations and determinations,” the White House writes.
The second layer entails the EO authorizing and directing the Attorney General to determine a Data Protection Review Court (DPRC) to “provide independent and binding review of the CLPO’s decisions, upon an application from the individual or an element of the Intelligence Community”.
Much will hinge on whether or not this physique will probably be correctly judged ‘court enough’ — beneath EU legislation — and subsequently competent to uphold and defend EU residents’ rights or not.
“Judges on the DPRC will be appointed from outside the US Government, have relevant experience in the fields of data privacy and national security, review cases independently, and enjoy protections against removal,” the White House writes. “Decisions of the DPRC relating to whether or not there was a violation of relevant US legislation and, if that’s the case, what remediation is to be carried out will probably be binding.
“To further enhance the DPRC’s review, the EO.provides for the DPRC to select a special advocate in each case who will advocate regarding the complainant’s interest in the matter and ensure that the DPRC is well-informed of the issues and the law with regard to the matter. The Attorney General today issued accompanying regulations on the establishment of the DPRC.”
The EO additionally calls on the (current) U.S. Privacy and Civil Liberties Oversight Board to evaluate the polices and procedures of U.S. spy companies to make sure consistency with what the order requires; and conduct an annual evaluate of the redress course of, together with to test whether or not intelligence companies have totally complied with determinations made by the CLPO and the DPRC.
“These steps will provide the European Commission with a basis to adopt a new adequacy determination, which will restore an important, accessible, and affordable data transfer mechanism under EU law. It will also provide greater legal certainty for companies using Standard Contractual Clauses and Binding Corporate Rules to transfer EU personal data to the United States,” the White House suggests.
Responding to the EO being signed, the Commission stated it accommodates “significant improvements” vs Privacy Shield’s mechanisms.
“At that time, individuals could turn to an Ombudsperson, which was part of the US State Department and did not have similar investigatory or binding decision-making powers,” it famous in a press launch.
“The objective of the Commission in these negotiations has been to address the concerns raised by the Court of Justice of the EU in the Schrems II judgment and provide a durable and reliable legal basis for transatlantic data flows. This is reflected in the safeguards included in the Executive Order, regarding both the substantive limitation on US national security authorities’ access to data (necessity and proportionality) and the establishment of the new redress mechanism,” it added.
Political settlement on a brand new EU-U.S. information transfers deal was introduced with a lot excessive stage fanfare, again in March.
EU commissioners had initially prompt the method is perhaps finalized by the top of this 12 months. However issues seems to have moved at a slower tempo than initially anticipated — so it now seems to be unlikely that every one the mandatory steps will probably be accomplished in time for the framework to be adopted earlier than 2023.
EU evaluate earlier than adoption
With Biden’s ink dry on the EO, the baton now passes again to the EU to think about whether or not the framework passes muster.
Various EU establishments will probably be concerned in reviewing the framework, together with the European Data Protection Board and representatives of Member States (and the European Parliament), though the ultimate choice is the Commission’s alone.
And the EU’s govt can — and sometimes does — override issues raised in the course of the evaluate course of (therefore two strikedowns already regardless of loads of objections raised to Privacy Shield previous to its adoption, in the latest instance… ).
The EU’s govt and the U.S. administration will each be eager for the brand new framework to stay and — ideally — show strong sufficient to see off any authorized challenges. But even when it solely sticks within the brief time period (a number of years) the prevailing view could also be that’s ‘fix’ sufficient — because it permits for ‘business as usual’ for cross-border information flows, getting each side out of a direct bind on the legality of trade-related information flows.
Tech giants, together with Facebook and Google, can even be crossing their pinkies that the DPF sticks — and rapidly — as each have been dealing with disruption to their companies and talent to serve clients within the area.
Facebook narrowly prevented a looming shutdown of its EU-U.S. information flows this summer season — after objections had been raised to a draft regulatory choice ordering them to be suspended, including months extra to the method (and probably sufficient time for it to keep away from a shutdown altogether if the EU adopts the DPF). So it’s now a race to see what lands first: The DPF or an order to Facebook to close off EU-to-U.S. information flows.
Google has additionally confronted disruption to its clients, following scores of complaints concentrating on customers of Google Analytics which led, in current months, to a variety of EU DPAs to warn towards use of the software in its commonplace configuration — saying such use breaches the EU’s General Data Protection Regulation and supplementary measures would must be utilized to boost the usual of information safety to the required stage.
Thousands of smaller companies additionally want authorized certainty round their cross-border information flows, after all. And tech business associations of all stripes had been fast to welcome the signing of the EO — and urge EU adoption swiftly.
An announcement by one business group — calling itself the Reform Government Surveillance coalition (whose members embody Amazon, Apple, Dropbox, Evernote, Google, Meta, Microsoft, Snap Inc., Twitter, Yahoo (TC’s father or mother), and Zoom) — welcomed the signing of the EO and what they dubbed its “robust new privacy protections”. However regardless of sporting a reputation with such a reforming-zeal vibe to it, the business foyer group didn’t name for extra root-and-branch adjustments to U.S. surveillance practices — as a substitute providing the flattering line that: “We recognize and appreciate the effort of the US Government in finalizing its implementation of the Framework.”
Other responses to the EO’s signing had been much less fulsomely welcoming.
BEUC, the European Consumer Organization, warned in an announcement that there are nonetheless “fundamental differences in the level of privacy and data protection in the US and the EU which remain too large to make up for, despite the additional safeguards the US side is proposing to build in” — and urged information safety authorities to “scrutinise any new data transfer agreement with rigour”. “Nobody wants more legal uncertainty,” it added. “We need a long-lasting solution to make sure consumers can trust that their data is safe wherever it goes.”
While Max Schrems, the lawyer and European privateness campaigner whose earlier authorized challenges introduced down Privacy Shield and Safe Harbor, warned that the settlement seems to be like a fudge — suggesting, for instance, that each side have agreed to make use of among the similar phrases however haven’t agreed on what the phrases imply, and arguing it could subsequently possible come unstuck beneath authorized scrutiny.
“The EU and the US now agree on use of the word ‘proportionate’ but seem to disagree on the meaning of it. In the end, the CJEU’s definition will prevail — likely killing any EU decision again. The European Commission is again turning a blind eye on US law, to allow continued spying on Europeans,” he stated in a response assertion, including: “We will analyze this package in detail, which will take a couple of days. At first sight it seems that the core issues were not solved and it will be back to the CJEU sooner or later.”
Schrems additionally pointed to the redress physique the EO establishes not being an actual court docket — which he stated is also an issue.
“We have to study the proposal in detail but at first glance, it is clear that this ‘court’ is simply not a court. The Charter has a clear requirement for ‘judicial redress’ — just renaming some complaints body a ‘court’ does not make it an actual court,” he stated. “The details of the procedure will also be relevant to see if this can satisfy EU law.”
“It is amazing that the EU and the US actually agree that wiretapping needs probable cause and judicial approval. However, the US takes the view that foreigners don’t have privacy rights,” Schrems added. “I doubt that the US has a future as the cloud provider of the world, if non-US persons have no rights under their laws. It is contradictory to me that the European Commission is working on a deal that accepts that Europeans are ‘second class’ citizens and don’t deserve the same privacy rights as US citizens.”
When/if the DPF is adopted by the Commission — almost certainly subsequent 12 months — authorized challenges stay extremely possible for the reason that basic conflict between U.S. national-security-focused surveillance legislation and EU basic privateness rights nonetheless hasn’t gone wherever.
Legal consultants will definitely be poring over the EO intimately as soon as they get their palms on the textual content.
“From the FactSheet: It is a solid improvement compared to 2016. But I want to also see the EO [text],” Dr. Gabriela Zanfir-Fortuna, VP for world privateness on the Washington-based thinktank, the Future of Privacy Forum, informed TechCrunch — providing a snap first response.
She additionally pointed to a line within the White House launch — by which the U.S. talks about “qualifying states” which it says will probably be “designated under the EO”, that means that the US will itself determine — positing that it is perhaps “looking at some form of reciprocity of sorts” within the nationwide safety space.
Edward Machin, a senior lawyer in Ropes & Gray’s information, privateness & cybersecurity follow, additionally informed TechCrunch: “We’re getting closer to European standards than under previous frameworks, although concerns remain about the long-term viability of an Executive Order. The proportionality and retention requirements look tighter and the older redress mechanism is improved. But it is enough? No one knows right now.”
Should a contemporary cycle of information switch litigation kick off, it should after all hold European privateness campaigners and information safety attorneys busy for years to come back.
They stay busy sufficient now, although, because the query of the place (and the way) EU customers’ information is saved stays a fear for companies exporting it to 3rd nations just like the U.S. that lack EU adequacy — with an actual prospect of regulatory enforcement in the mean time.
Further rounds of regulatory whack-a-mole would even be inevitable if this ‘third time lucky’ framework topples, restarting the info switch criticism cycle as soon as once more. So we are able to all most likely anticipate to be again in a contemporary authorized limbo quickly sufficient.
This report was up to date with extra remark.
Source link
#President #Biden #indicators #govt #order #aimed #authorized #reboot #EUUS #information #flows


